Single sign-on and directory sync
Let a team sign in with its company identity provider and keep membership in step with your directory, using OpenID Connect and SCIM 2.0
Single sign-on and directory sync are an add-on on Scale ($149 per month), self-serve from Billing → Add-ons, and included with Enterprise. Once the add-on is on, the settings below appear on the Team page (Settings → Team → Open Team) for the workspace owner. Both are owner-only, and workspaces without the add-on don't see them. See Add-ons for billing details.
Single sign-on
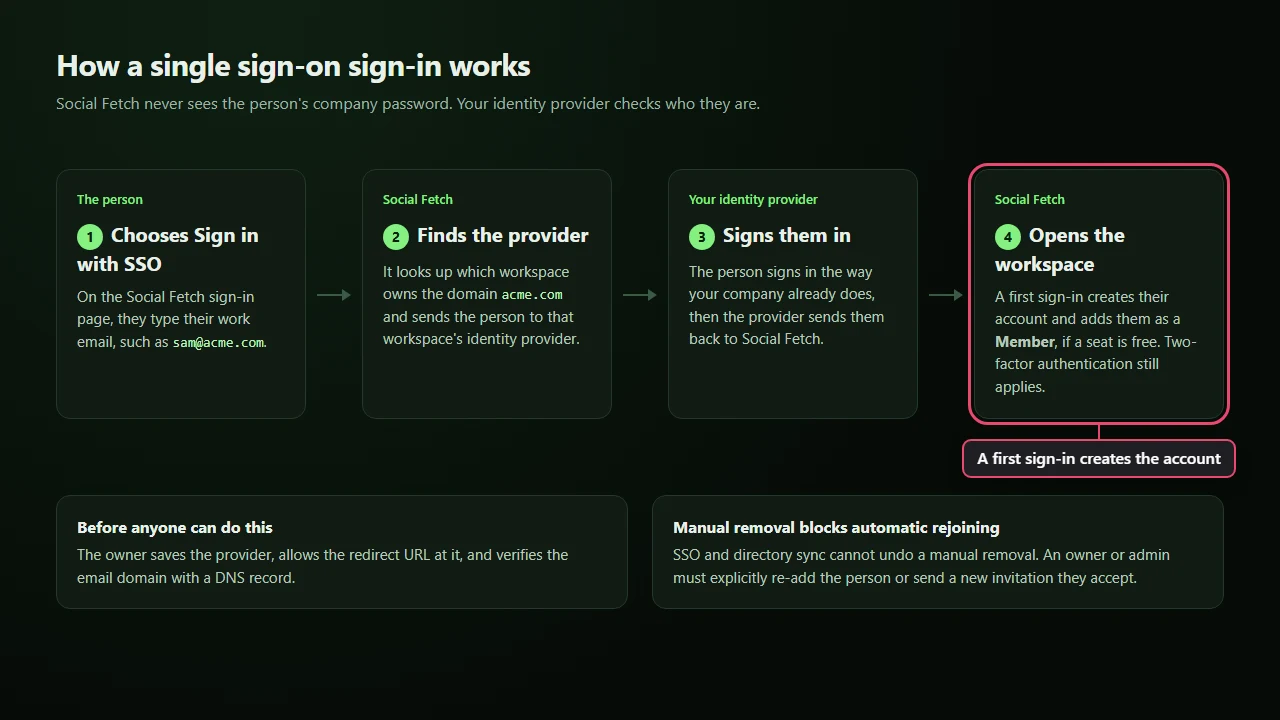
Social Fetch supports single sign-on over OpenID Connect, which Okta, Microsoft Entra ID, Google Workspace and most other providers offer. Each workspace can register one provider. Here is what happens when someone signs in:
Set up
- At your identity provider, create an application for Social Fetch. It will ask for a redirect URL, which Social Fetch shows in step 3, so keep it open.
- In Social Fetch, open the Team page and find Single sign-on. Enter your provider's Issuer URL, your company Email domain, the Client ID and the Client secret, then choose Save provider. Add a Discovery URL only if your provider's isn't the issuer URL followed by
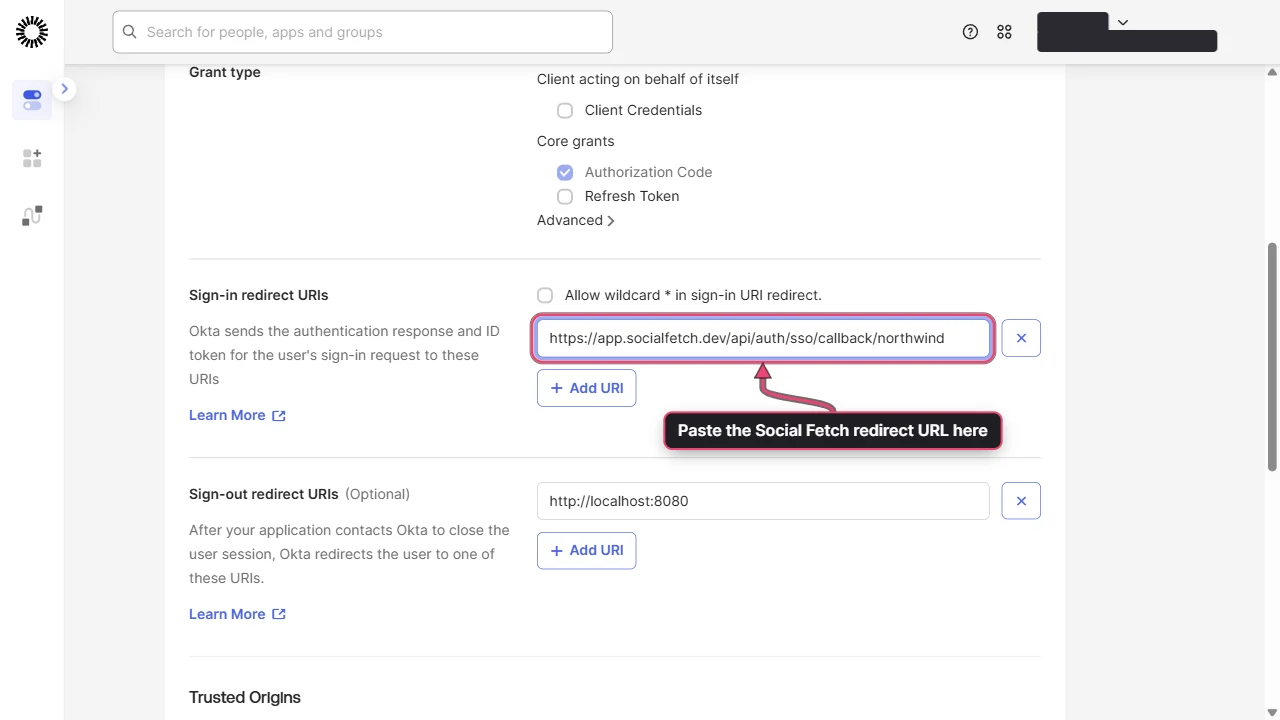
/.well-known/openid-configuration. Provider endpoints must usehttpson the default port (443) at a public host. - Copy the Redirect URL to allow at your provider that now shows, and allow it in the application you created (in Okta, Sign-in redirect URIs).
- Add the DNS
TXTrecord shown under Verify (a Host and a Value) to your domain to prove you own it, then choose Verify. DNS changes can take a few minutes to appear. If the code runs out, choose New code. The code is valid for 7 days. Nobody can sign in through the provider before this succeeds, and one domain can belong to one workspace.
Signing in
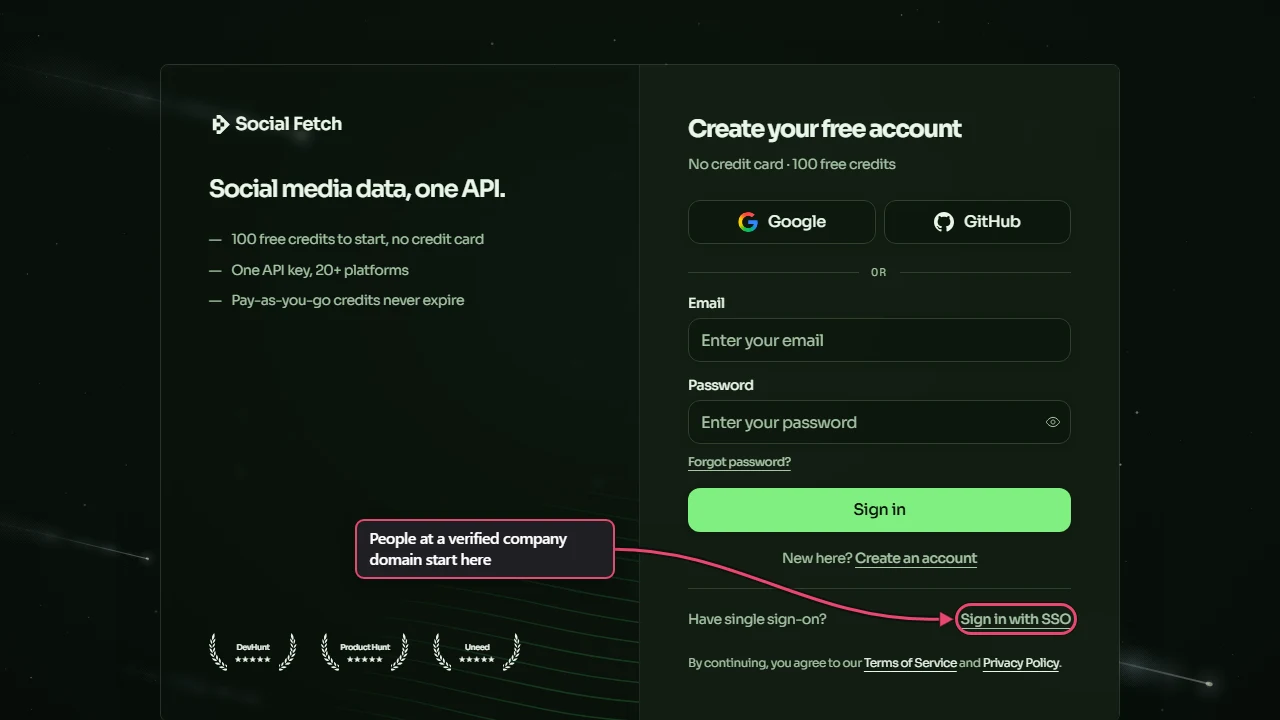
People with an email at the verified domain choose Sign in with SSO on the sign-in page, type their work email and choose Continue with SSO. Their first sign-in creates their account and adds them to the workspace as a Member. This uses the same seat limit as invitations; if the workspace is full, they see that there are no free seats. Owners raise roles afterwards. Accounts with two-factor authentication still complete their second step.
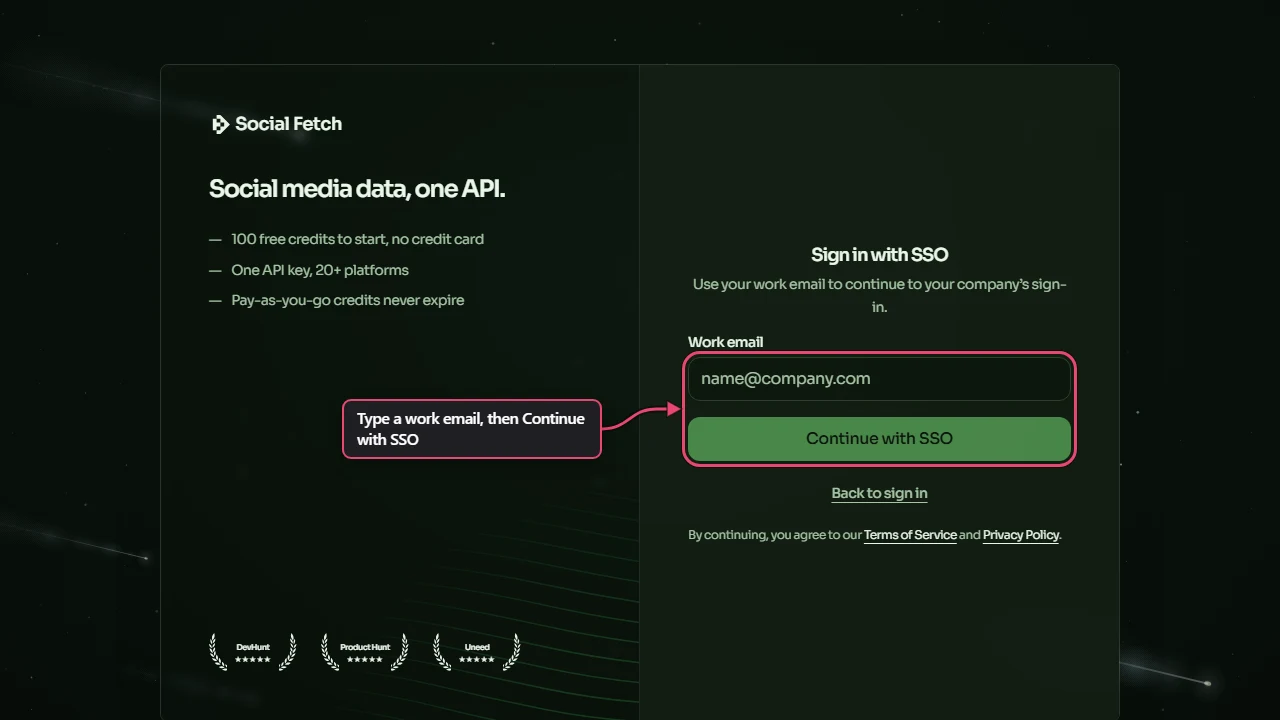
If the address isn't at a verified domain, they see "Single sign-on isn't set up for that address" and can use another way to sign in.
Require SSO
Once the domain is verified and you have signed in through the provider yourself, an owner can turn on Require single sign-on for this workspace and confirm with Require it. The switch stays off, with the reason beneath it, until both are true. From then on:
- Members without an SSO session get
403 forbiddenwithreason: sso_requiredfor that workspace, and the dashboard sends them to a page explaining why. - AI app (MCP) connections need a live SSO session.
- API keys are unaffected.
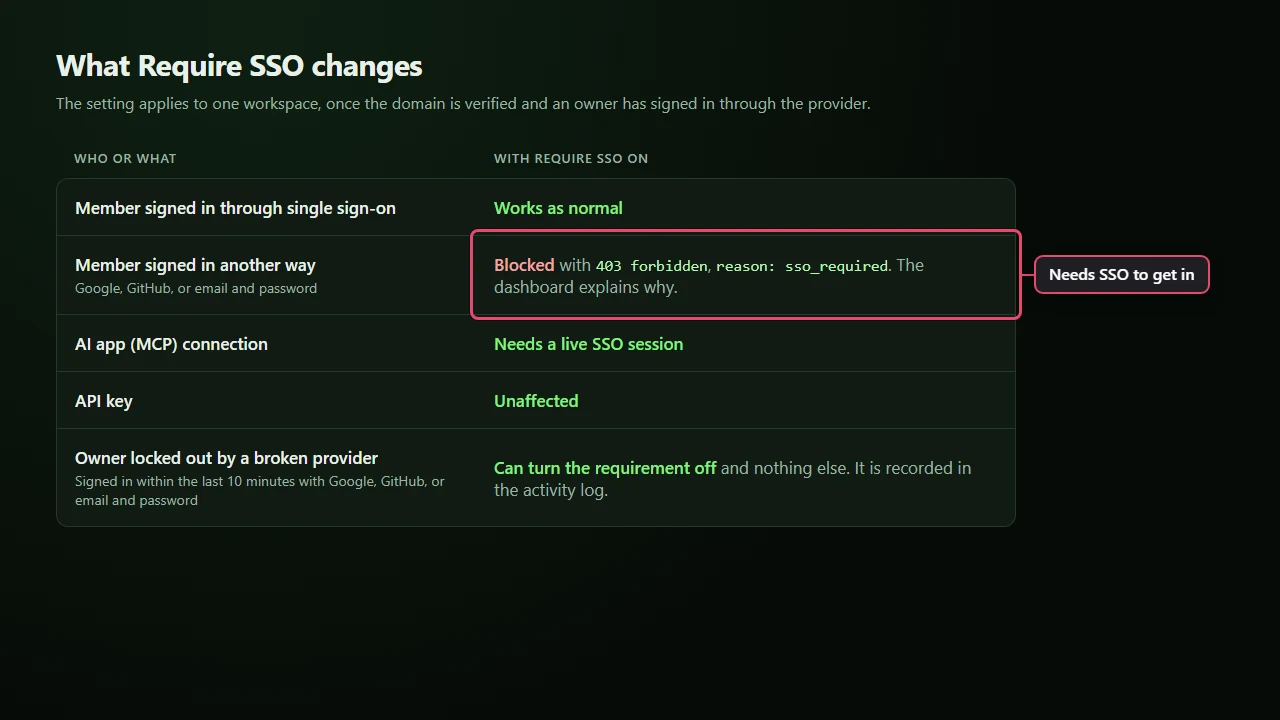
If your provider breaks while this is on, an owner can sign in with Google, GitHub, or email and password (the sign-in must be under 10 minutes old) and open the workspace. The page explaining that single sign-on is required has an Owner recovery box with a Turn off required single sign-on button. This only lets them turn the requirement off, and it is recorded in the activity log.
To stop using single sign-on, turn the requirement off first, then choose Remove under Remove provider. Members keep their accounts and their place in the workspace.
Removing someone from the workspace blocks automatic rejoining through both single sign-on and directory sync. To bring them back, an owner or admin must explicitly re-add them or send a new invitation that they accept. Their provider access is separate and should also be removed when they leave your company.
Someone who leaves the workspace themselves is not blocked. They can rejoin through SSO if the provider still lets them sign in and a seat is free. Directory deprovisioning is different: SSO cannot restore their access while the directory lists them as inactive. Reactivate them through directory sync to restore access, subject to the seat limit.
Directory sync (SCIM 2.0)
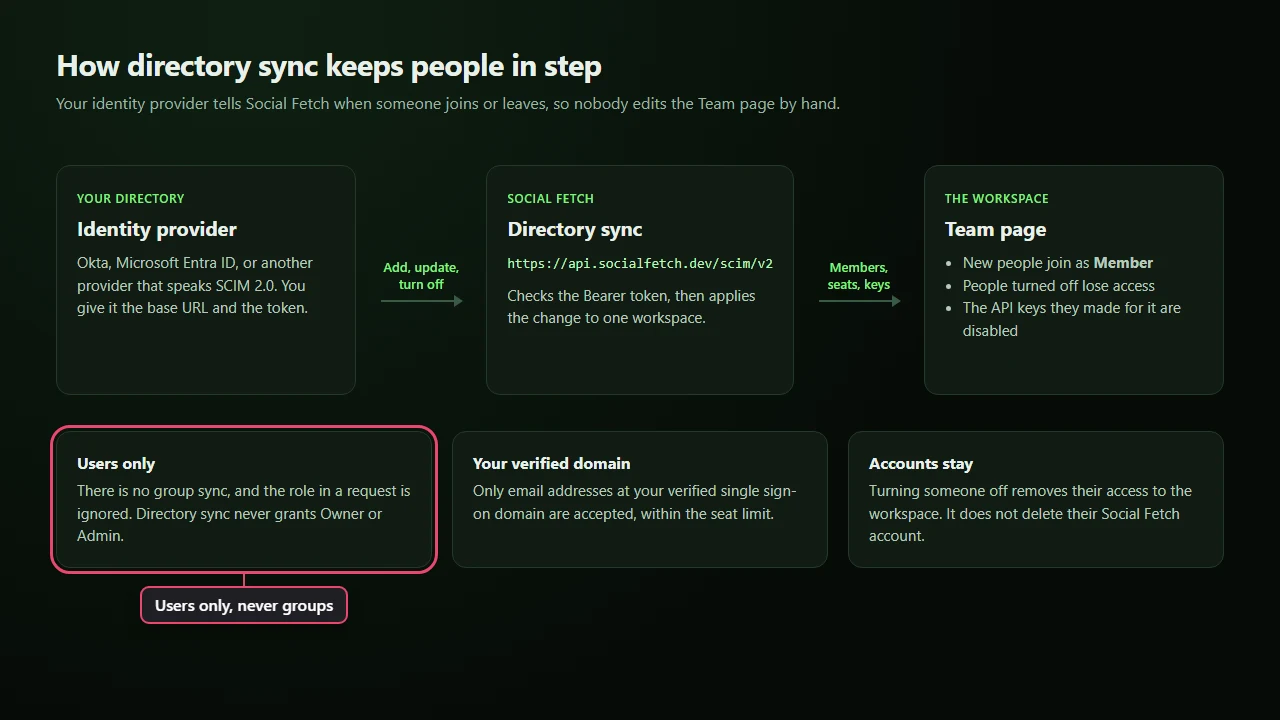
Directory sync automatically adds and removes workspace members based on changes sent by your identity provider (such as Okta or Microsoft Entra ID). It handles users only, not groups, and needs a verified single sign-on domain.
Set up
- On the Team page, find Directory sync and choose Generate token. The token is shown once, so copy it.
- In your identity provider's SCIM settings, enter the base URL shown on the page (
https://api.socialfetch.dev/scim/v2) and the token as a Bearer token.
Replace makes a new token and the old one stops working at once. Revoke deletes it; everyone keeps their access.
What it does
| Operation | Behaviour |
|---|---|
Create user (POST /Users) | Adds the person as a Member, within the seat limit. Only addresses at your verified single sign-on domain are accepted. Roles in the request are ignored; directory sync never grants Owner or Admin. |
| Read, list, filter | GET /Users and GET /Users/{id}. Filters: userName, externalId, id, active with eq. Pages hold up to 100. |
Update (PUT, PATCH) | Updates names and the active flag. The email can't be changed. |
Deactivate (active: false) or DELETE | Removes their access to the workspace and disables the API keys they made for it. Their account is not deleted. SSO cannot rejoin them while they are inactive. Setting active: true again clears a directory deprovisioning block and restores access if a seat is free. It cannot override a manual removal; that needs an explicit re-add or an accepted new invitation. |
Owners can't be deprovisioned; change their role on the Team page first. Discovery endpoints (/ServiceProviderConfig, /ResourceTypes, /Schemas) are available for provider set-up.
Teams and workspaces
Share one balance, one set of API keys and one bill with your team. Roles, invitations, seats, and how requests are attributed.
Overview
Connect Social Fetch to your tools. Use MCP in AI clients, n8n, Make, Pipedream or Apify for automations, or call the TypeScript SDK and REST API from your own code.